Most small businesses have never made an active decision about endpoint security. What’s running on a given laptop or phone is whatever came pre-installed, whatever an IT vendor set up years ago, or whatever an employee added on their own. That configuration became the default and stayed the default, because revisiting it was never anyone’s assigned job.
Endpoint security covers every device that connects to business systems and the protections applied to each one: antivirus and malware detection, patch management, encryption, access controls, and increasingly, monitoring tools that flag unusual behavior in real time. The concept itself is straightforward. What breaks down in practice is ownership: who keeps it current, consistent, and enforced across every device in the business.
What “protected” usually means in practice
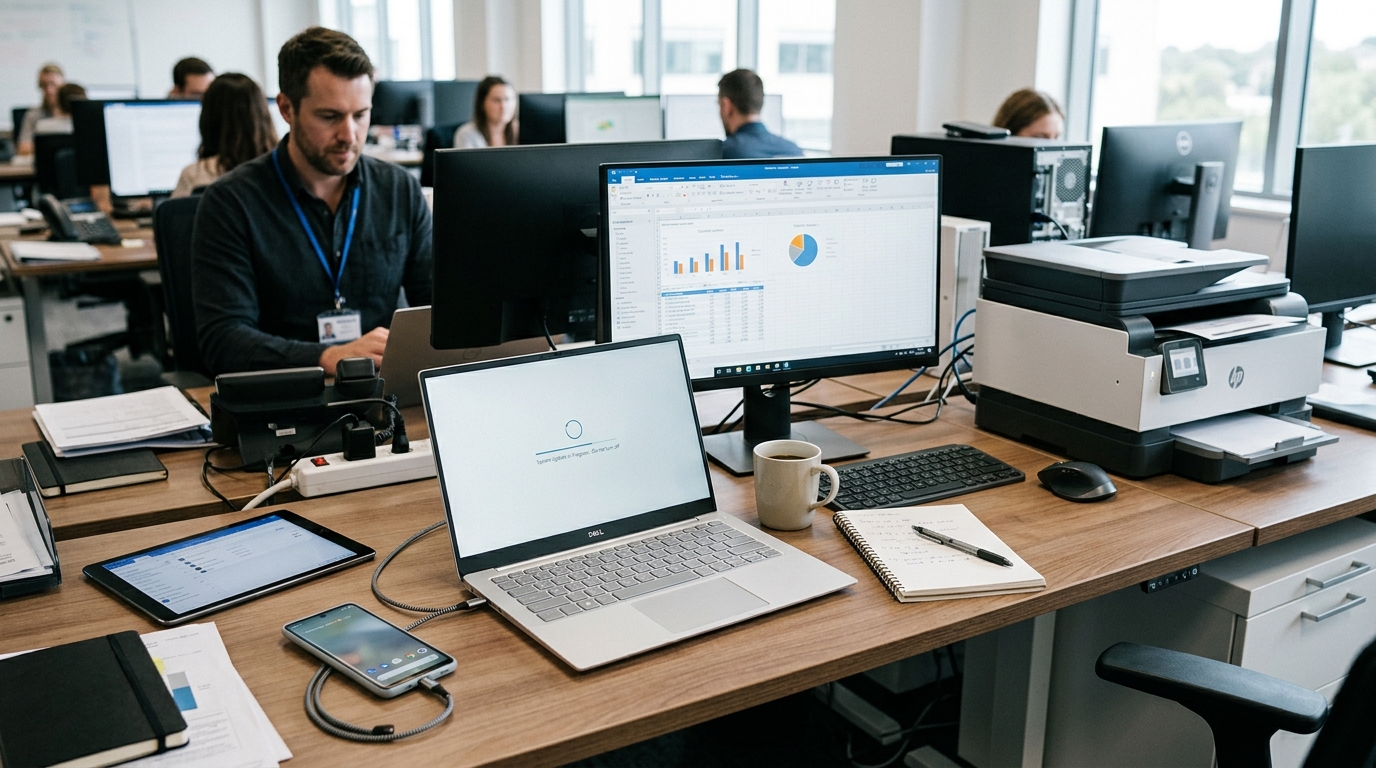
Walk through the devices at a typical small business and the protection picture rarely looks intentional. A front-desk computer running the antivirus that came bundled with Windows. A sales laptop with a personal security app an employee installed at home years ago and never removed. A finance manager’s phone checking company email with no passcode requirement enforced. A printer or camera still running the factory credentials it shipped with, never reset.
Each of these devices is “protected” in the loosest sense. Something is technically running. But protection that arrived by accident is not the same as protection that was evaluated and chosen for the risk it’s meant to cover.
Basic antivirus catches known threats by matching them against a database of previously identified malware. It does very little against attacks that don’t match a known signature, which describes a growing share of what actually compromises small businesses today.
The distance between “something is installed” and “this is actively managed” is where most small business endpoint security lives. That distance tends to be invisible until an incident forces someone to ask what was actually running on the affected device.
Ownership needs to get assigned on purpose
Ask most small business owners who is responsible for endpoint security, and the honest answer is usually a shrug in the direction of IT, whether that’s an internal employee wearing five hats or an outside vendor handling break-fix requests. IT ends up owning it by default, without anyone formally assigning the responsibility.
This matters because endpoint security requires ongoing attention. Patch schedules need active enforcement, beyond simply being available. Access permissions need periodic review as employees change roles or leave.
New devices, personal phones, vendor laptops, smart office equipment, need to be brought under the same standard as everything else. Each of these depends on someone doing the check on a schedule, and in most small businesses, that job was never explicitly assigned to anyone.
The 2025 Verizon Data Breach Investigations Report found ransomware present in a large majority of breaches affecting small and mid-sized businesses, a notably higher share than at larger organizations. Larger companies are more likely to have someone whose job includes catching a lapse before it turns into an incident. Most small businesses have no one in that role at all.
One standard, applied everywhere
For a business owner, what matters is whether the same standard applies to every device that touches company data, regardless of which employee set it up or when. That standard matters more than which antivirus brand happens to be running.
A consistent standard means every device follows the same patch cadence, applies encryption to company data regardless of whether the device is company-issued or personal, and closes a departing employee’s access the same day they leave. It also means something is actively monitoring for unusual activity across the network on an ongoing basis.
What matters is a standard applied the same way every time, with a person or team accountable for making sure it holds. Without that accountability, tools drift out of compliance. Licenses lapse. Settings get changed to accommodate one urgent request and never get reverted. A device gets added to the network without anyone circling back to bring it under policy.
Three questions worth asking
A business with clear ownership over endpoint security can answer a short set of questions without hesitation. Which devices are currently under active monitoring, and which aren’t. When was patch compliance last verified, and how was that confirmed. Who gets notified when a device falls out of compliance, and how fast does that get resolved.
Uncertain answers to those questions point to the real problem. Endpoint security usually fails because responsibility for maintaining it was never clearly placed on anyone’s desk. The product chosen rarely has much to do with it.
For businesses relying on one internal employee juggling IT alongside other responsibilities, this pattern is common, and it says more about workload than intent. Endpoint security requires ongoing attention that competes with daily operational demands, and something usually loses that competition. The solution is a structure where monitoring and enforcement run independent of whether one already-stretched employee remembers to check that week.
Putting one standard behind every device
At Syntech Group, endpoint security is treated as an ongoing responsibility: every device connecting to a client’s systems, company-issued or personal, is brought under one consistent standard, monitored continuously, patched on schedule, and reviewed as part of regular operations.
If your business can’t currently say who owns endpoint security, or what happens when a device falls out of compliance, reach out. We’ll walk through what’s currently protecting your systems and assign clear ownership over keeping it that way.